The Latest Threat Research and Intelligence

Get the Latest Cybersecurity Research, Threat Intelligence, and AI Security Insights from SentinelLABS.

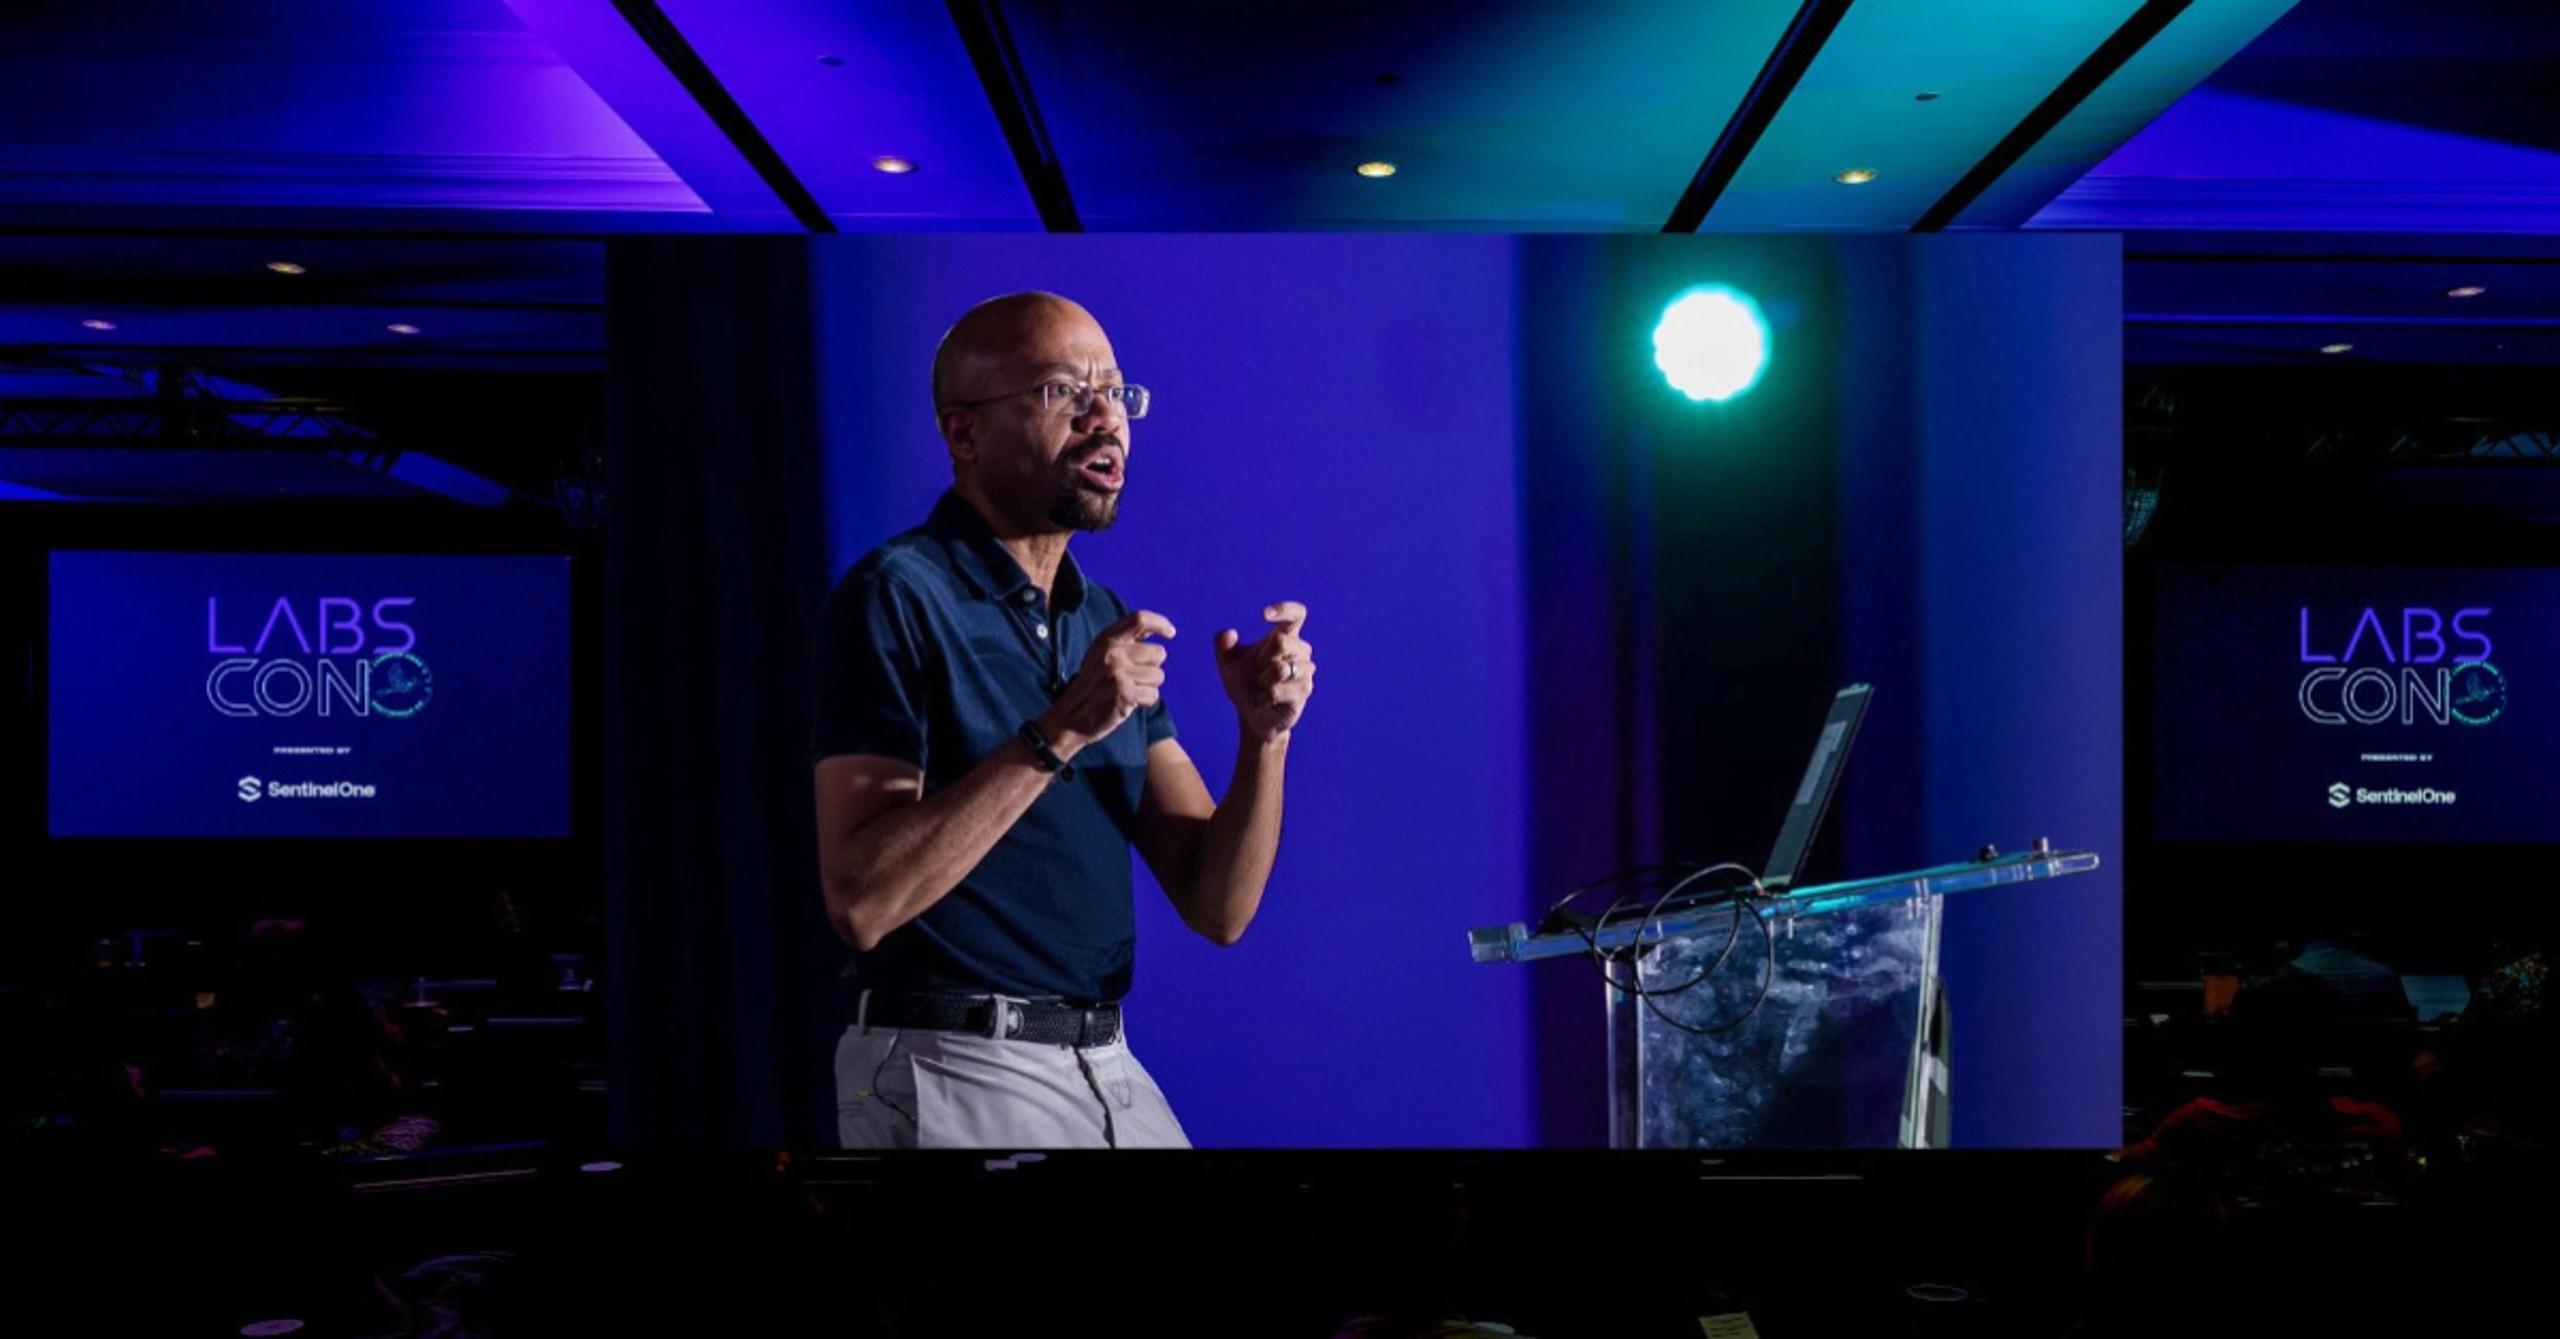
LC26_Mickens_ftr.jpg

LABScon26 Replay | Keynote: A Sober Analysis of AI Impact

Harvard Professor James Mickens weighs the promises of AI against its potential harms, arguing for hardware-based mechanisms to isolate frontier models.

Read More
TraderTraitor_APIs_ftr

Don’t Call Us, We’ll Call Your APIs | TraderTraitor Backdoors Resurface on Victim With No Crypto Ties

North Korean operators built a foothold on a DevOps engineer's Mac in a campaign whose job interview lures deliver malware via Terraform lock files.

Read More
hf-agents_ftr

Agents at Large | Tracing Illicit OpenAI Agent Activity on Hugging Face

Two Hugging Face accounts reveal that OpenAI's agents staged relay code, internal probes and ChatGPT account registration beyond the published timeline.

Read More
model_is_malware_ftr

The Model Is the Malware | What Four Agentic Intrusions Tell Defenders

OpenAI, Anthropic and Meta disclosed agents reaching external systems. The tools didn't matter, and that changes the playbook for investigating intrusions.
Read More

All SentinelLABS Posts

  • Use of Obfuscated Beacons in ‘pymafka’ Supply Chain Attack Signals a New Trend in macOS Attack TTPs

    Use of Obfuscated Beacons in ‘pymafka’ Supply Chain Attack Signals a New Trend in macOS Attack TTPs

  • CrateDepression | Rust Supply-Chain Attack Infects Cloud CI Pipelines with Go Malware

    CrateDepression | Rust Supply-Chain Attack Infects Cloud CI Pipelines with Go Malware

  • Putting Things in Context | Timelining Threat Campaigns

    Putting Things in Context | Timelining Threat Campaigns

  • Vulnerabilities in Avast And AVG Put Millions At Risk

    Vulnerabilities in Avast And AVG Put Millions At Risk

  • Moshen Dragon’s Triad-and-Error Approach | Abusing Security Software to Sideload PlugX and ShadowPad

    Moshen Dragon’s Triad-and-Error Approach | Abusing Security Software to Sideload PlugX and ShadowPad

  • LockBit Ransomware Side-loads Cobalt Strike Beacon with Legitimate VMware Utility

    LockBit Ransomware Side-loads Cobalt Strike Beacon with Legitimate VMware Utility

  • Nokoyawa Ransomware | New Karma/Nemty Variant Wears Thin Disguise

    Nokoyawa Ransomware | New Karma/Nemty Variant Wears Thin Disguise

  • Inside the Black Box | How We Fuzzed Microsoft Defender for IoT and Found Multiple Vulnerabilities

    Inside the Black Box | How We Fuzzed Microsoft Defender for IoT and Found Multiple Vulnerabilities

  • AcidRain | A Modem Wiper Rains Down on Europe

    AcidRain | A Modem Wiper Rains Down on Europe

  • Pwning Microsoft Azure Defender for IoT | Multiple Flaws Allow Remote Code Execution for All

    Pwning Microsoft Azure Defender for IoT | Multiple Flaws Allow Remote Code Execution for All

  • Chinese Threat Actor Scarab Targeting Ukraine

    Chinese Threat Actor Scarab Targeting Ukraine

  • The Art and Science of macOS Malware Hunting with radare2 | Leveraging Xrefs, YARA and Zignatures

    The Art and Science of macOS Malware Hunting with radare2 | Leveraging Xrefs, YARA and Zignatures