The Latest Threat Research and Intelligence

Get the Latest Cybersecurity Research, Threat Intelligence, and AI Security Insights from SentinelLABS.

LC26_Mickens_ftr.jpg

LABScon26 Replay | Keynote: A Sober Analysis of AI Impact

Harvard Professor James Mickens weighs the promises of AI against its potential harms, arguing for hardware-based mechanisms to isolate frontier models.

Read More
TraderTraitor_APIs_ftr

Don’t Call Us, We’ll Call Your APIs | TraderTraitor Backdoors Resurface on Victim With No Crypto Ties

North Korean operators built a foothold on a DevOps engineer's Mac in a campaign whose job interview lures deliver malware via Terraform lock files.

Read More
hf-agents_ftr

Agents at Large | Tracing Illicit OpenAI Agent Activity on Hugging Face

Two Hugging Face accounts reveal that OpenAI's agents staged relay code, internal probes and ChatGPT account registration beyond the published timeline.

Read More
model_is_malware_ftr

The Model Is the Malware | What Four Agentic Intrusions Tell Defenders

OpenAI, Anthropic and Meta disclosed agents reaching external systems. The tools didn't matter, and that changes the playbook for investigating intrusions.
Read More

All SentinelLABS Posts

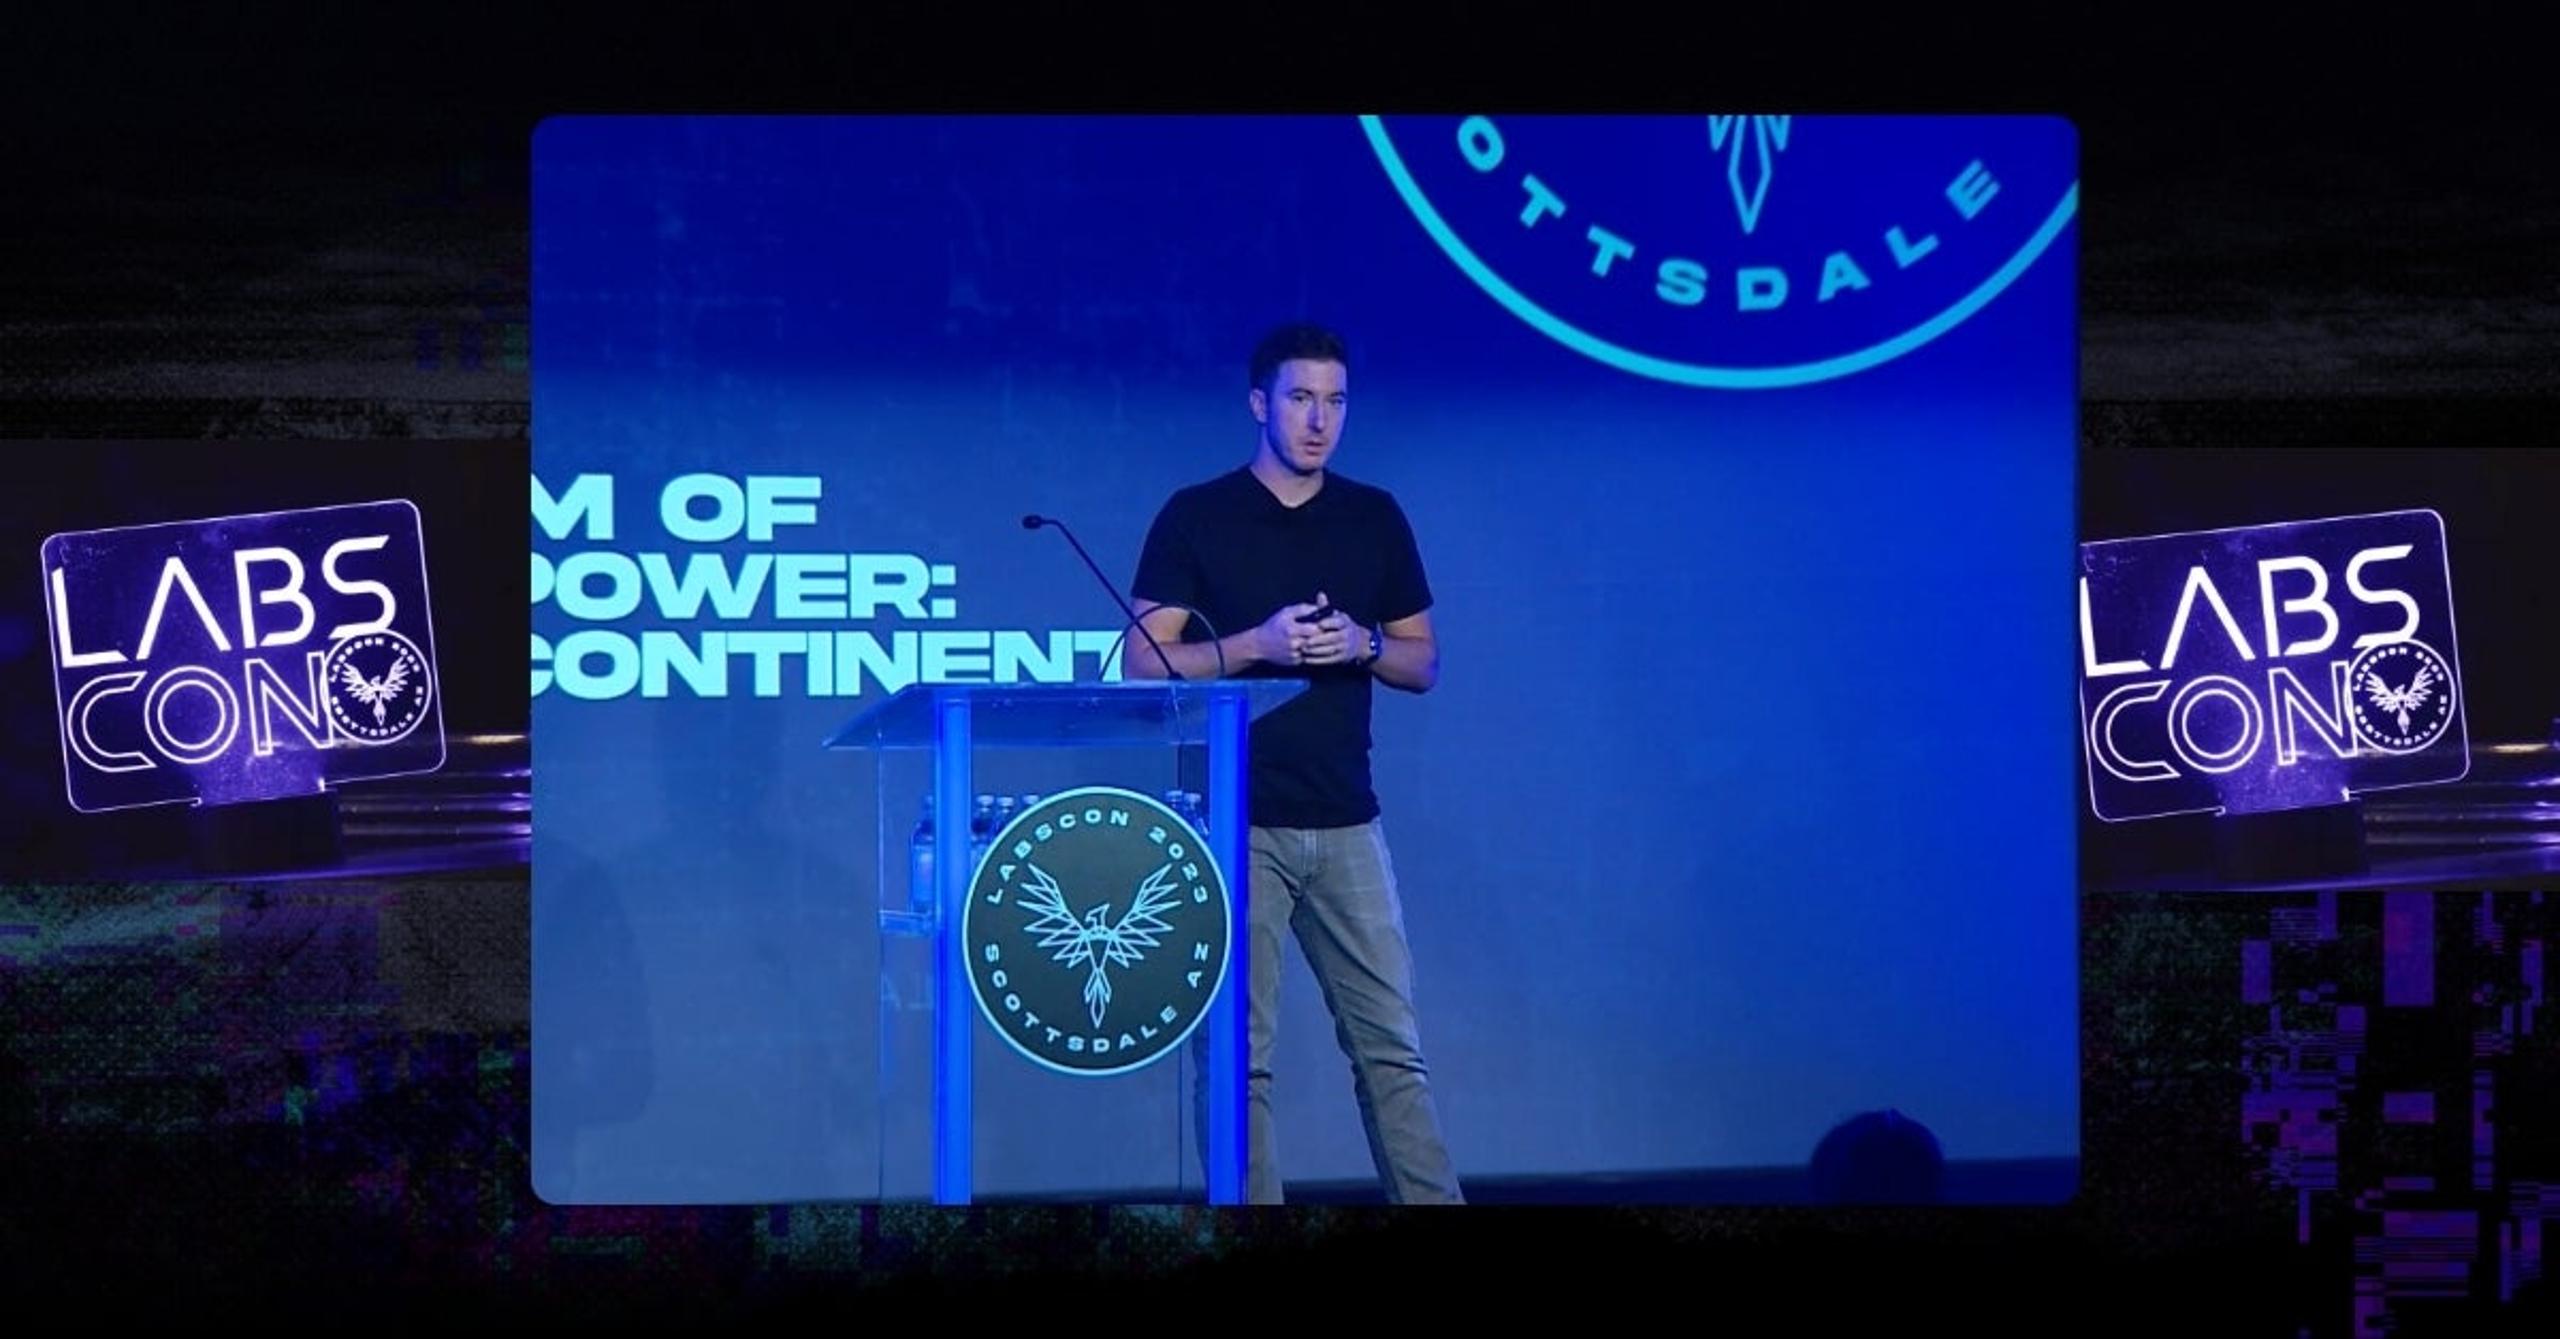
  • LABScon Replay | The Cyber Arm of China's Soft Power: Reshaping a Continent

    LABScon Replay | The Cyber Arm of China's Soft Power: Reshaping a Continent

  • Decoding the Past, Securing the Future | Enhancing Cyber Defense with Historical Threat Intelligence 

    Decoding the Past, Securing the Future | Enhancing Cyber Defense with Historical Threat Intelligence 

  • Elephant Hunting | Inside an Indian Hack-For-Hire Group

    Elephant Hunting | Inside an Indian Hack-For-Hire Group

  • Predator AI | ChatGPT-Powered Infostealer Takes Aim at Cloud Platforms

    Predator AI | ChatGPT-Powered Infostealer Takes Aim at Cloud Platforms

  • Arid Viper | APT’s Nest of SpyC23 Malware Continues to Target Android Devices

    Arid Viper | APT’s Nest of SpyC23 Malware Continues to Target Android Devices

  • 11 Ways to Tweak radare2 for Faster and Easier macOS Malware Analysis

    11 Ways to Tweak radare2 for Faster and Easier macOS Malware Analysis

  • The Israel-Hamas War | Cyber Domain State-Sponsored Activity of Interest

    The Israel-Hamas War | Cyber Domain State-Sponsored Activity of Interest

  • Sandman APT | A Mystery Group Targeting Telcos with a LuaJIT Toolkit

    Sandman APT | A Mystery Group Targeting Telcos with a LuaJIT Toolkit

  • Cyber Soft Power | China's Continental Takeover

    Cyber Soft Power | China's Continental Takeover

  • CapraTube | Transparent Tribe’s CapraRAT Mimics YouTube to Hijack Android Phones

    CapraTube | Transparent Tribe’s CapraRAT Mimics YouTube to Hijack Android Phones

  • Bloated Binaries | How to Detect and Analyze Large macOS Malware Files

    Bloated Binaries | How to Detect and Analyze Large macOS Malware Files

  • Chinese Entanglement | DLL Hijacking in the Asian Gambling Sector

    Chinese Entanglement | DLL Hijacking in the Asian Gambling Sector