The Good, the Bad and the Ugly in Cybersecurity - Week 44 (2026)
The Good | Global Response Continues for PHP2SHELL Exploit Attempts & Defenders Dismantle Global Cybercrime Rings
This past week, cyber defenders responded to a cluster of vulnerability disclosures and security incidents collectively dubbed “Black October,” spanning flaws in PHP2SHELL, Node.js, GitLab, and Brotli, a software supply chain attack in LiteLLM, and compromised certificate authority keys at eMudhra.
Despite PHP2SHELL affecting roughly 70% of websites worldwide, mass, internet-wide exploitation of the kind seen with Log4SHELL hasn’t materialized. PHP2SHELL lacks a universal offset, since heap layouts, memory alignments, and worker states differ by PHP version, build, and SAPI configuration, and attackers must craft specific request streams to line up memory blocks before triggering the underlying out-of-memory error.
That complexity hasn’t stopped targeted compromises against systems, but it has kept broad, automated attacks from succeeding at scale. CISA added both PHP2SHELL CVEs to its Known Exploited Vulnerabilities catalog, with a remediation deadline of October 29 for federal agencies.
International law enforcement this week also delivered major blows against cybercrime syndicates. Authorities extradited Chinese national Zheng Zhao from the Netherlands to California over an alleged multimillion-dollar cryptocurrency investment scheme that defrauded 174 American victims through fake trading platforms.
A U.S. federal court sentenced Ukrainian national Artem Stryzhak to 70 months in prison for conspiring to deploy Nefilim and Hive ransomware against hospitals, law firms, and other targets.
Finally, an international law enforcement coalition seized the domain of Virtualine, a “bulletproof” hosting provider that marketed itself to criminals for “all illegal/black hat activities”. Court records tie the seizure to Virtualine hosting child sexual abuse material (CSAM) and non-consensual intimate imagery despite repeated takedown notices, plus money laundering that concealed the proceeds. Virtualine had also offered to quietly migrate a customer’s infrastructure to a shell company after law enforcement made contact.
The Bad | Threat Actors Chain Fragnesia Linux Flaw with PHP2SHELL to Root PAN-OS Firewalls
As part of Black October, researchers are warning that a high-severity Linux kernel privilege escalation flaw is being actively chained with the PHP2SHELL vulnerabilities. Tracked as CVE-2026-46300 and dubbed “Fragnesia,” the flaw stems from a logic defect in the Linux XFRM ESP-in-TCP subsystem that leaves stale page-cache writes exploitable for root access. Public proof-of-concept exploits allow local attackers to execute arbitrary code with root permissions on major Linux distributions running kernels released before May 13, 2026.
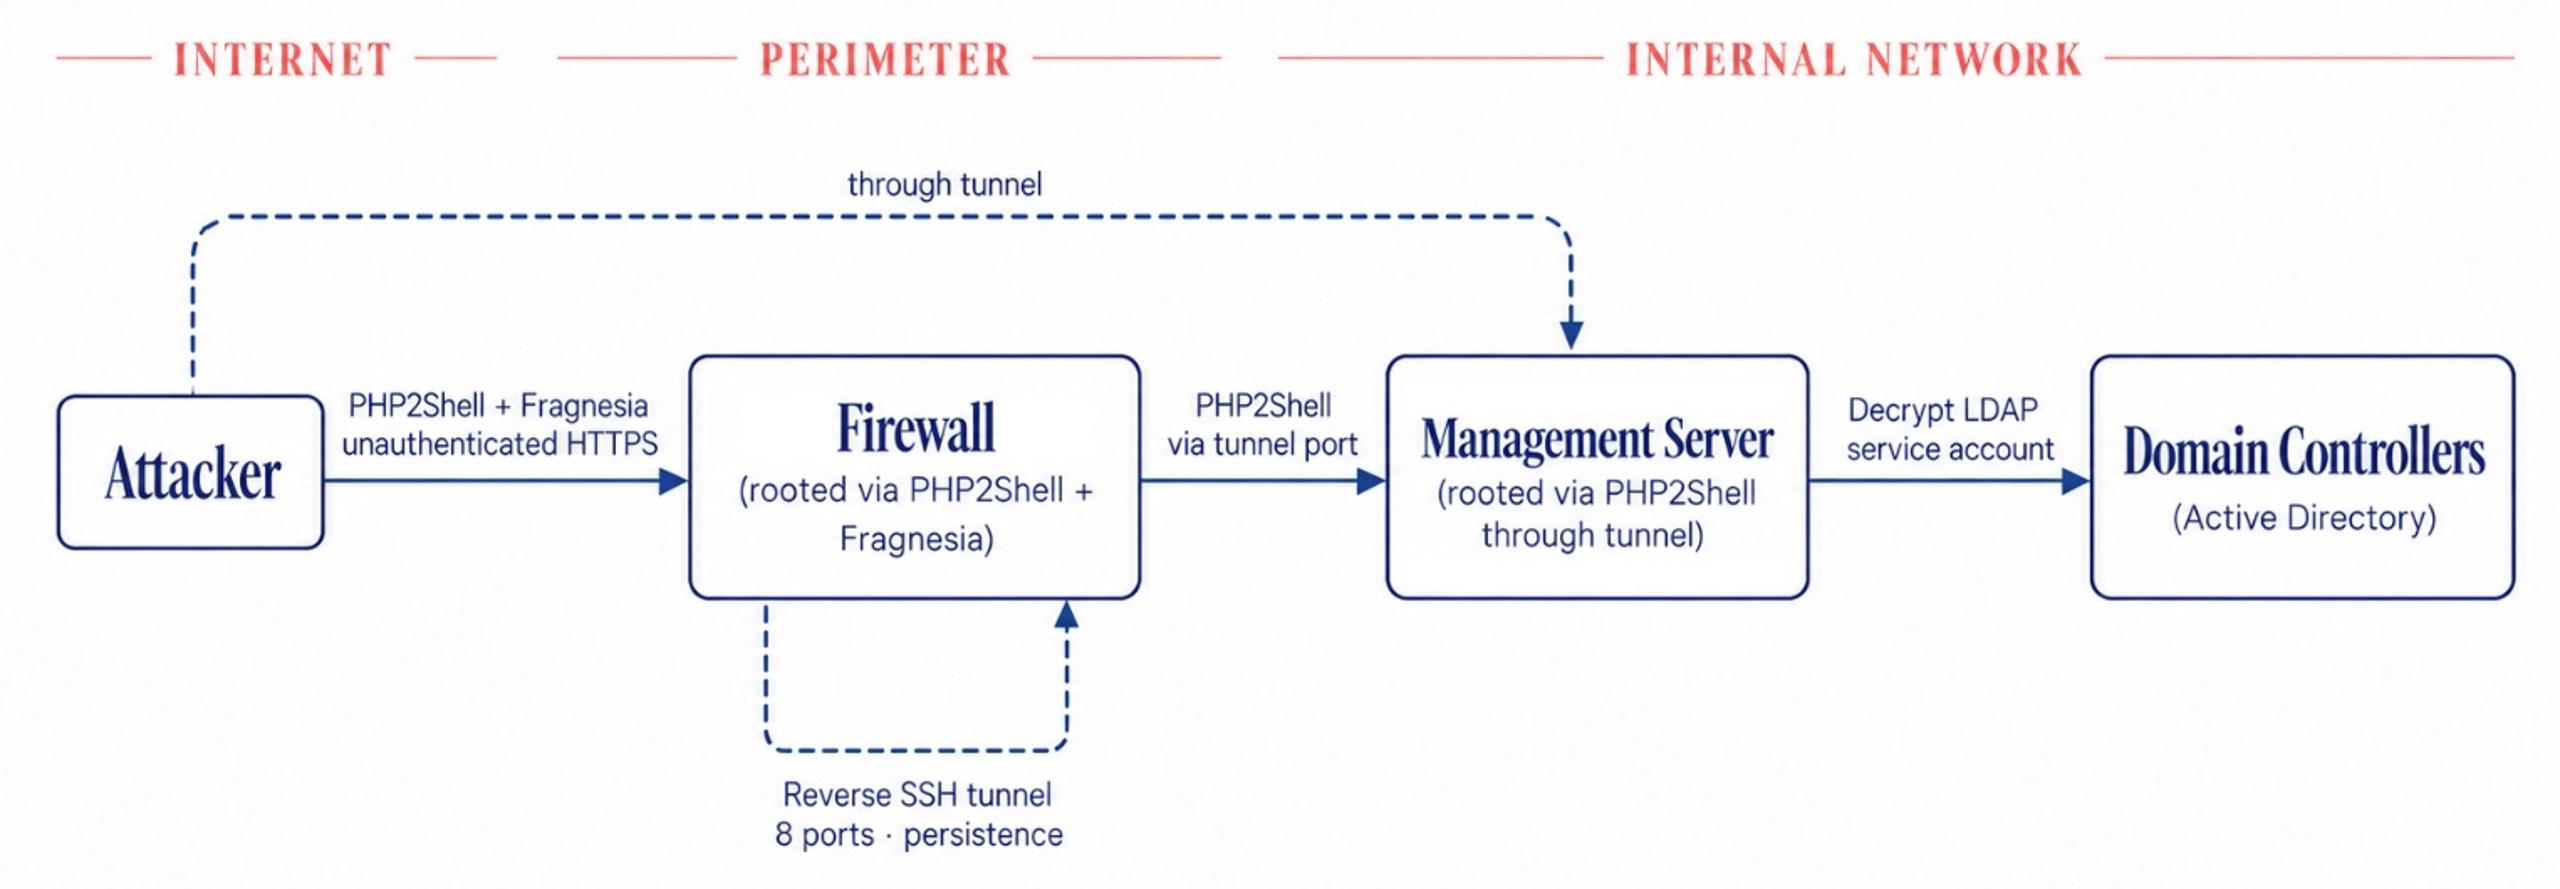
In response to active in-the-wild exploitation, CISA added Fragnesia to the KEV Catalog and mandated federal agencies patch affected systems under Binding Operational Directive 26-04, noting that threat actors are pairing it with the PHP2SHELL RCE flaws: exploiting PHP2SHELL first to implant a web shell, then using Fragnesia to escalate from that shell to full root control.
Security researchers uncovered a complete attack operation featuring custom weaponized exploit chains, target lists, detailed activity logs, and roughly 40 custom post-exploitation scripts. The campaign successfully rooted 25 PAN-OS firewall and management servers, whose web interface runs on PHP, across the United States, Japan, Taiwan, and South Korea, including three systems in a U.S. government-affiliated environment.
Chaining an unauthenticated web flaw with a local kernel privilege escalation means patching either one alone isn’t enough. Closing the web shell’s entry point still leaves the root escalation path open on any system running a vulnerable kernel.
The Ugly | Silent Fix for Brotli Decoder Exposes Node2Shell Vulnerability
Security researchers uncovered a critical memory corruption vulnerability in the open-source Brotli compression decoder used across much of the web. Tracked as CVE-2026-111497 with a CVSS score of 9.2, the flaw, variously named Node2Shell, HTTP2Shell, and Broccoli2Shell by the researchers who worked on it, stems from an out-of-bounds write when handling invalid stream block switches during decompression. It affects Brotli versions 1.0.3 through 1.2.0, reaching major language runtimes and web frameworks including Node.js, Python, and .NET.
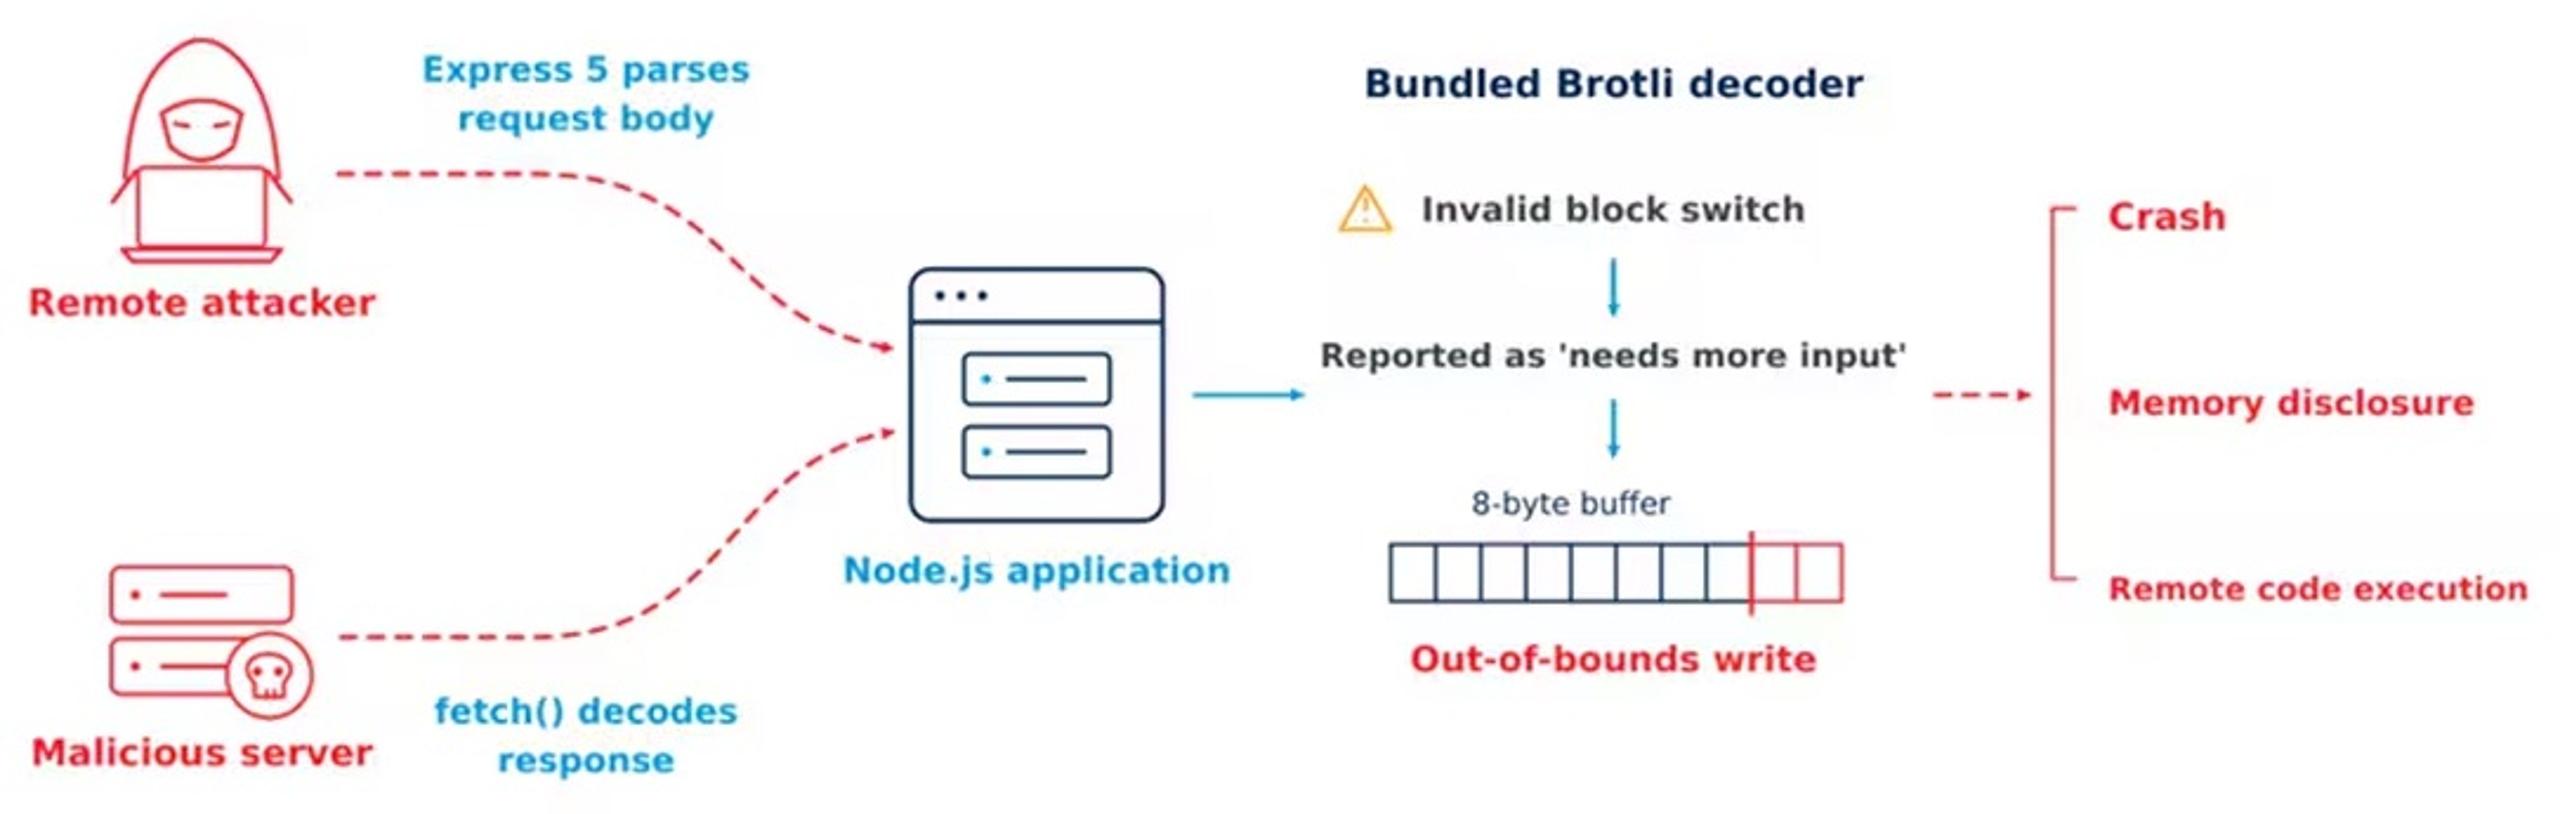
The flaw’s timeline stretches back further than its public disclosure. Upstream developers quietly fixed the underlying code on February 27 without a security advisory or CVE, and the vulnerability wasn’t publicly identified until a researcher team reported it in October.
Coordinated disclosure landed October 21, and fixes followed in waves: Python’s package registry shipped updates October 22 and 23, a Ruby gem update followed October 24, and .NET received an out-of-band patch on October 25, the same day researchers demonstrated working code execution on x86-64 against Node.js. Separate research into FFmpeg the same day produced a reproducible crash rather than confirmed code execution. Edge and hosting providers rolled out interim firewall mitigations within hours of the initial disclosure.
CISA added CVE-2026-111497 to its KEV catalog on October 27, requiring federal remediation by November 10. Because proxy-level filtering doesn’t protect outbound client requests or file-based attack paths, closing this gap means upgrading the underlying Brotli library and rebuilding affected applications, not just patching at the network edge.
Watch the GBU Highlights
Related Articles